Background
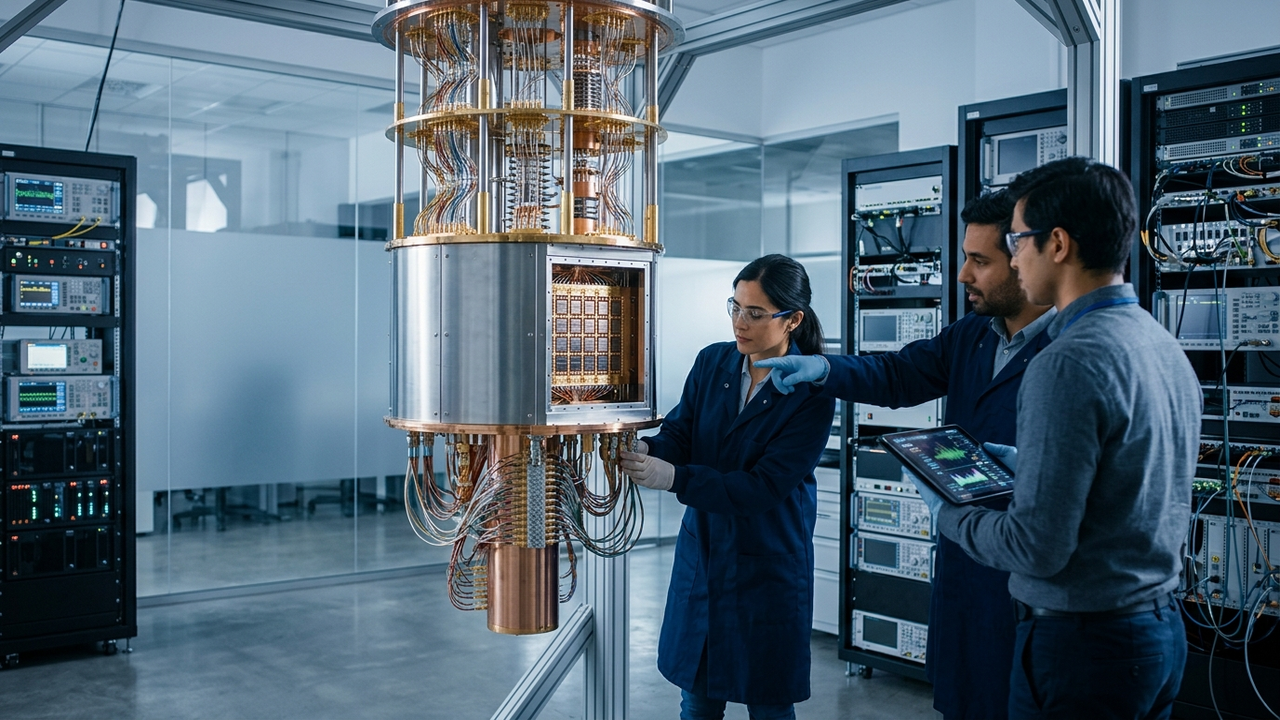
The global cybersecurity community is engaged in a critical race against time, striving to transition to post-quantum cryptography (PQC) before large-scale quantum computers can render current encryption standards obsolete. The specter of ‘Q-Day’—the moment when fault-tolerant quantum computers become capable of effectively compromising widely used public-key cryptography—looms ever closer. While past estimates suggested that breaking conventional encryption would necessitate an enormous number of stable, error-corrected qubits, rapid advancements in both theoretical and practical quantum error correction (QEC) techniques are drastically lowering this threshold. This progress fundamentally reshapes the projected timeline for practical quantum computing and carries profound implications for national security, global financial systems, and personal data privacy. Major players in quantum computing, including IBM, are actively investigating advanced QEC paradigms.
Key Findings
Significant advancements in quantum error correction (QEC), most notably driven by the emergence of quantum low-density parity-check (qLDPC) codes, are rapidly accelerating the development of practical quantum codebreaking capabilities. These innovative QEC paradigms indicate that prevailing cryptographic standards such as 256-bit elliptic-curve cryptography (ECC-256) and RSA-2048 could potentially be compromised with a substantially reduced number of physical qubits compared to previous estimates.
qLDPC codes provide an exceptionally efficient mechanism for safeguarding fragile quantum information from decoherence and gate errors. These codes are particularly well-suited for physical qubit platforms like trapped-ion and neutral-atom qubits, where precise individual qubit control is more readily achievable. A seminal research paper from Caltech, published in March 2026, proposed a neutral-atom quantum computer architecture specifically incorporating qLDPC-based error correction. Simulations from this groundbreaking study indicate that such an architecture could potentially break ECC-256 encryption with a mere 10,000 physical qubits and RSA-2048 encryption with 100,000 physical qubits. This represents a remarkable reduction in the physical qubit overhead previously thought necessary for such cryptanalytic feats, profoundly impacting the timeline for practical quantum computing.
The accelerated research and implementation of qLDPC codes are set to expedite the development of fault-tolerant quantum computers, making the urgent transition to more robust, quantum-resistant cryptography even more critical. Researchers and engineers will increasingly capitalize on these new error correction techniques to hasten the construction of practical quantum machines. Concurrently, enterprises and government agencies face heightened pressure to rapidly upgrade their existing cryptographic infrastructures to be quantum-safe, safeguarding against the imminent capabilities of advanced quantum codebreaking.
Source: https://orfme.org/expert-speak/quantum-codebreaking-moves-one-step-forward/
Get our weekly technology intelligence — free
Receive an infographic that lets you judge at a glance whether each field’s analysis report is worth reading.
Subscribe Free — Weekly Tech Intelligence
By subscribing, you’ll receive Troy-Technical’s weekly technology intelligence newsletter.
- Your email and selected fields are used only to deliver the newsletter.
- We never share your information with third parties.
- You can unsubscribe anytime via the link in each email.
See our Privacy Policy for details.
Takes about a minute · Unsubscribe anytime

Comments